Cybersecurity Services · Parramatta
Cybersecurity for Parramatta: Prioritise Practical Business Controls
Build a practical cybersecurity improvement plan for your Parramatta business. OnIT Solutions helps review access, devices, email and recovery readiness so decisions reflect the systems you actually use.
No lock-in · Sydney-based engineers · Response <4h

<0h
Response SLA
Priority response in Parramatta
0%
Uptime Target
SLA-backed availability
0
Lock-In Contracts
Cancel anytime, no penalties
0%
Australian Team
Local engineers, no offshore
Technology partners and platforms we work with


What we deliver
Cybersecurity Services that works while you do.
Everything your Parramatta business needs — managed as one seamless service with a fixed monthly price and guaranteed response times.
Last updated: 30 September 2026
A cybersecurity review should produce decisions
A useful cybersecurity engagement starts with the business's systems and exposure, then turns findings into an ordered set of actions. OnIT Solutions helps small and medium-sized businesses reduce risk through practical controls, including multi-factor authentication, endpoint protection, email security, patching, device management and backup readiness. For a Parramatta business, the first conversation should identify important information, the accounts that can reach it and the effect of an interruption. That gives a security review a clear purpose without assuming every organisation needs the same tools or the same implementation sequence.
Ask for findings to explain the affected system, the potential consequence, the recommended action and who must approve it. A long list of technical settings is difficult to use if the business cannot distinguish urgent gaps from planned improvements. Include known constraints, such as an older application or a third-party supplier that manages part of the environment. Security changes can affect access and normal work, so priorities should consider both exposure and implementation requirements. The aim is to make informed choices and reduce risk, rather than claim that any review can establish perfect security.
Start with identities and access permissions
An account can be a route into several business systems, which makes identity a sensible starting point. Review who has access, which accounts have administrative privileges and whether former staff or unused accounts remain active. OnIT can assist with MFA setup and enforcement as well as security reviews. Before changing access requirements, establish which applications and devices are involved and how staff will enrol or recover access. A control that users cannot follow safely can create confusion, so implementation should include clear instructions and a defined support route for genuine access problems.
Shared access deserves particular attention. A team may need a shared mailbox or collaborative documents without sharing a personal password. Identify the business owner who approves permissions and review whether access matches current roles. Where suppliers administer systems, understand their responsibilities and the permissions they retain. Record approved changes and review dates so access decisions are not lost when staff change. These steps are relevant to a Parramatta organisation using cloud services or business applications, but the actual permissions and configuration should be assessed in its own environment rather than copied from a generic checklist.

Combine device protection with patching and email controls
Endpoint protection is one layer of defence, rather than a substitute for keeping devices managed. OnIT's cybersecurity services include endpoint protection, patching and device management, while its broader service information describes threat monitoring and endpoint detection and response. Ask which devices are covered, what happens when a device stops reporting and who reviews alerts. Include laptops used away from the office when they access business information. A device inventory helps the business understand whether coverage follows its actual equipment, rather than only the machines that happen to be visible during an initial review.
Email security should consider both technical controls and staff decisions. Messages can exploit urgency, impersonate a colleague or persuade someone to approve a payment or sign-in request. OnIT can help with email protection and user security awareness. Discuss how suspicious messages should be reported and how staff can verify sensitive requests through an established channel. Training should relate to your team's work, without promising that awareness alone prevents every attack. Technical configuration, account controls and consistent reporting all contribute to reducing the chance that a misleading message becomes a wider business incident.
Treat recovery readiness as a security question
Security planning must consider the possibility that prevention fails. Backup readiness is part of OnIT's published capabilities, and a review should ask what information can be recovered, which systems are included and how the recovery process is checked. A successful backup notification does not explain every recovery limitation. Different applications may store data in different places or require their own restoration steps. Identify the business functions that must resume first, then use that information to discuss priorities and whether the existing protection is suitable for the environment.
An incident reporting route should also be agreed before a problem appears. Staff need to know whom to contact if they suspect an email breach, lost device or unexpected access. Describe the affected system and observed symptoms to OnIT through the official support channel. Avoid trying destructive fixes or circulating sensitive evidence widely while seeking help. The immediate objective is to obtain appropriate assistance and preserve a clear account of events. Any response work and recovery expectations should be agreed for the circumstances; a routine security service is not an unconditional guarantee of recovery.

Move from review to an accountable improvement plan
OnIT's published cybersecurity capabilities include work with the ACSC Essential Eight mitigation strategies. If that framework is relevant to your requirements, ask which controls are being assessed and how implementation evidence will be documented. A discussion of a framework should not be treated as automatic certification or proof of compliance with every obligation. Your business's requirements may depend on contracts, information handled and industry obligations. Bring those requirements into the review so the technical work can be scoped appropriately and any need for additional professional advice or specialist assessment is identified.
For the first assessment, prepare a list of users, devices, important applications, administrative accounts and existing security or backup arrangements. State any concerns, previous incidents and requirements from customers or suppliers without sending sensitive credentials. Ask for a prioritised improvement plan, named responsibilities and a way to confirm completed work. Parramatta businesses can then decide whether they need a focused security review, particular control implementation or ongoing managed support. Review the remaining risks as systems change. The useful outcome is better visibility and a practical sequence of improvements that the business can understand and maintain.
Quick Facts
“For Parramatta businesses, cybersecurity services isn't just about keeping things running — it's about building a technology foundation that drives growth across Western Sydney.”
— OnIT Solutions, Western Sydney

What's included
Cybersecurity Services in Parramatta. One team.
ACSC Essential 8 Compliance
We implement the Australian Government's Essential 8 mitigation strategies to harden your environment.
Endpoint Detection & Response
Advanced EDR tools detect and isolate threats before they spread — with real-time alerts and remediation.
24/7 Threat Monitoring
Continuous monitoring of your network, endpoints, and email for threats, with rapid incident response.
Security Audits & Testing
Thorough vulnerability assessments and security audits that identify gaps before attackers do.
Service detail
Full-spectrum protection, one team
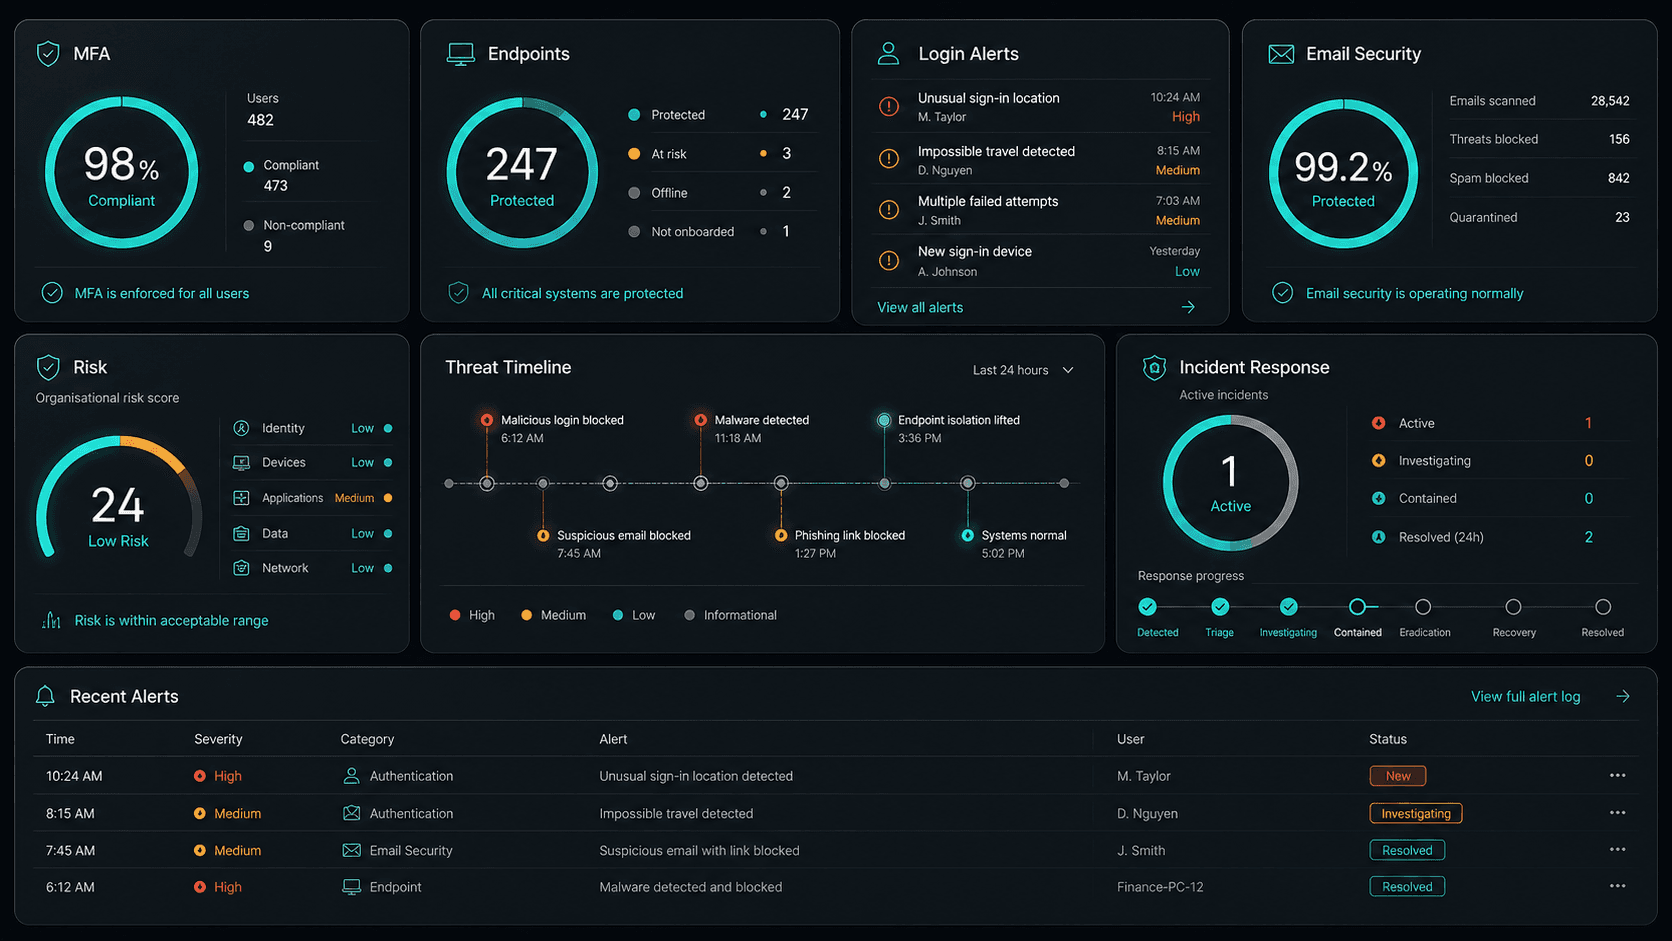
24/7 automated threat monitoring across endpoints, network, and email — incidents contained before they escalate.
CrowdStrike and Microsoft Defender deployed across all devices — real-time detection, automated isolation, and forensic logging.
Entra ID, MFA enforcement, conditional access policies, and privileged access management — zero-trust ready.
Continuous scanning, prioritised patching, and Essential Eight alignment — known risks eliminated before they're exploited.
Advanced email filtering, anti-spoofing, and phishing simulation training — your team's most common attack vector, locked down.
Staff phishing simulations and security awareness programs — turning your people into a human firewall.
Documented IR playbooks, tabletop exercises, and breach response retainer — so you're never starting from zero.
Essential Eight, ISO 27001, and industry-specific compliance reporting — audit-ready documentation maintained year-round.
Why OnIT
Everything in one cybersecurity service
One provider. One invoice. Threat monitoring, compliance, and endpoint protection — all covered.
24/7 threat monitoring
Automated alerts watch your network, endpoints, and email around the clock — catching threats before they escalate.
Enterprise security stack
CrowdStrike, Defender, Fortinet, Cloudflare — best-in-class security platforms all managed under one fee.


Sydney-based security team
Local security engineers on-site across Greater Sydney, with remote incident response available 24/7.
Essential Eight compliance
ACSC Essential Eight implementation, continuous patching, MFA enforcement, and EDR — always maintained.



Technology Ecosystem
Powered by Enterprise Technology
A constellation of best-in-class platforms, deployed and managed as one seamless service.
Enterprise platforms we deploy and manage


Service Breakdown
What's inside your plan
Click any card to see exactly what's included in each service area.

Cybersecurity Services that scales from 5 to 200 seats, across every Western Sydney business.
Why OnIT Solutions
Your Parramatta business, without the overhead.
Serving Parramatta (2150) and the broader Western Sydney area — our Sydney-based engineers understand the Western Sydney business community and are reachable when you need them. Whether you're a 5-person team or a growing operation with 200 seats, we scale cybersecurity services to fit.
By the numbers
Measurable outcomes, guaranteed in writing
No surprise invoices. No waiting on hold. No different technician every time you call.
At a Glance
Included in your plan
Got questions?
Frequently asked questions
Also serving nearby
Cybersecurity Services across Western Sydney
Explore further
Related services for Parramatta
IT Support Sydney
On-demand helpdesk and on-site support for your team. Fast response, local engineers, no lock-in contracts.
AI Automation
Workflow automation, AI chatbots and voice agents that reduce admin and free your team to focus on growth.
Managed IT
Proactive IT management with 24/7 monitoring, patching, and helpdesk support for your entire team.

Get started
Ready for better Cybersecurity Services
in Parramatta?
Book a free cybersecurity services assessment with one of our Sydney-based engineers serving Parramatta and Western Sydney. No lock-in, no obligation.
No lock-in contracts · Sydney-based engineers · Same-day response